

Ampath has cautioned against claims that 80 million patient records were affected by a cybersecurity incident, saying the figure may refer to database entries rather than individual patients as its investigation into the breach continues, Cape {town}Etc reports.
The pathology laboratory group confirmed that the incident affected part of its information technology environment but said there was, to date, no evidence that patient medical records, diagnoses, pathology results or banking information had been compromised.
In a media statement issued earlier today, Ampath said the investigation, supported by independent cyber forensic specialists and legal advisers, was still under way to establish the full scope and impact of the incident.
The company said information potentially affected appeared to be limited to certain personal demographic and related administrative details, although these findings were still being verified.
Ampath also challenged the interpretation of the widely circulated figure of 80 million records, arguing that it should not be taken as the number of individual patients whose information may have been affected.
‘The publicly cited number appears to refer to database records or entries (data rows) rather than unique individuals,’ the statement said.
The company explained that one patient can generate multiple records over years of interactions with a healthcare provider. These may include registrations, account updates, administrative details, transactions and other entries associated with the same person.
Ampath said it believed the figure being circulated materially overstated the number of individuals potentially affected and urged the public not to treat claims made by threat actors as verified findings.
The actual number of people affected has not been confirmed in the statement.
Ampath said it detected the incident on 2 October and immediately activated its incident response procedures.
The measures taken included blocking malicious IP addresses, restricting access to affected systems, disabling exposed accounts and credentials, removing unauthorised files and restoring systems from clean backups.
The company also said it addressed identified vulnerabilities, strengthened application and access controls, introduced additional endpoint security measures and conducted security testing and vulnerability scans.
Ampath confirmed that it had notified the Information Regulator and was cooperating with the relevant authorities.
It added that there was no evidence of ongoing unauthorised access, while cybersecurity specialists continued to assess forensic evidence and monitor its systems.
Despite the investigation, Ampath stated that its laboratories, pathology services and patient care operations remained fully functional, with no disruption to service delivery.
The company acknowledged that reports of a cybersecurity incident could cause concern among patients, healthcare professionals and other stakeholders, but stressed that information about the breach should be based on verified forensic findings rather than unconfirmed claims.
This caution follows an earlier report which detailed how a criminal group known as ByteToBreach claimed to have stolen millions of patient records from Ampath, raising alarms across the healthcare sector about data security risks.
The investigation remains ongoing, and Ampath said it would provide further updates as verified information becomes available.
Be the first to know – Join our WhatsApp Channel for content worth tapping into! Click here to join!
Also read:
Massive police data breach raises national security alarm in South Africa
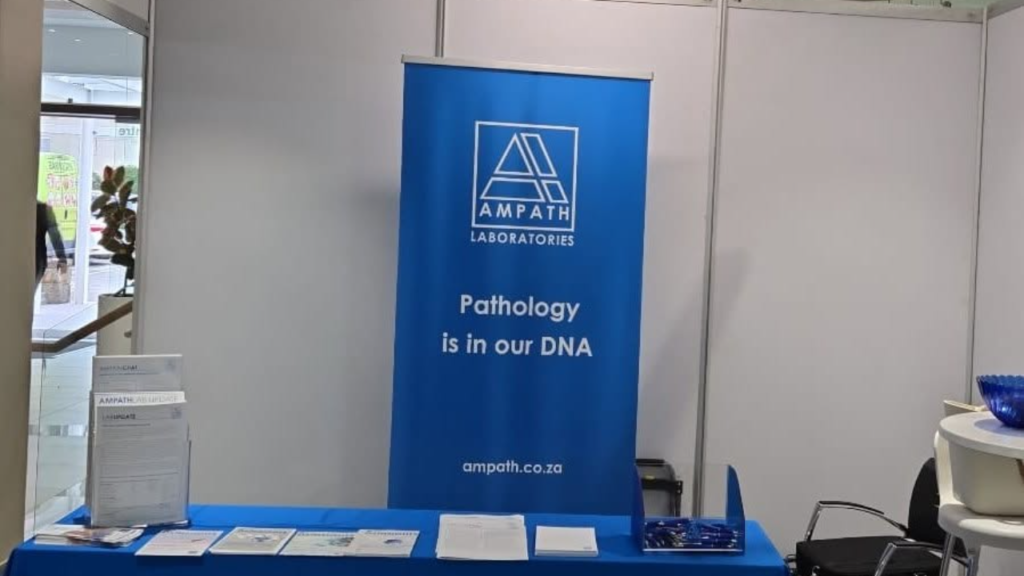
Picture: Ampath Laboratories / Facebook